Solutions
Strong Customer Authentication (SCA)
Understanding SCA and its impact on frictionless payments in Europe
SCA requirements under PSD2
In 2019 a requirement to require multi-factor authentication for e-commerce transactions were introduced in Europe by the revised Payment Services Directive (PSD2). Strong Customer Authentication (SCA) was initiated to increase the security of electronic payments through requiring customers to provide two forms of identification when shopping online:
What the cardholder knows:
e.g., a PIN code or a password
What the cardholder has:
e.g., a phone, a tablet or a token
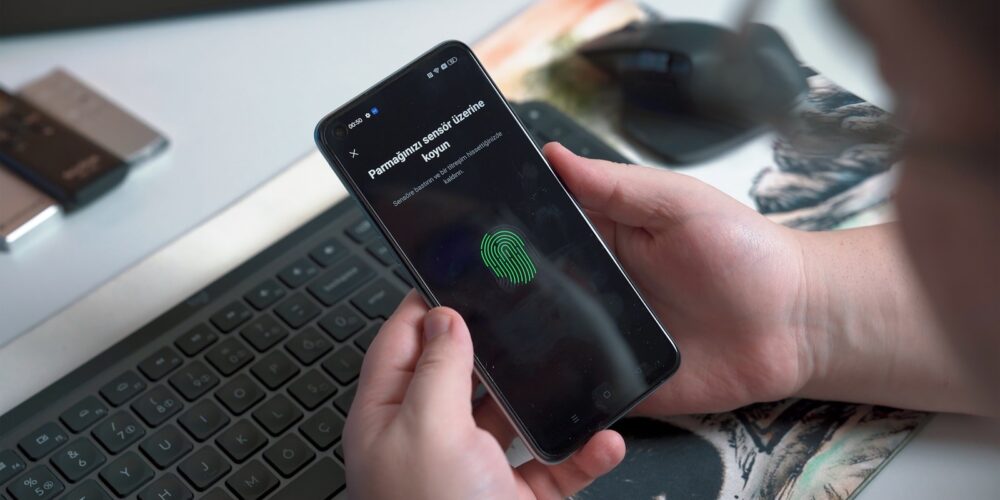
Who the cardholder is:
e.g., a fingerprint or facial recognition
Before SCA, payments were authorized using only one piece of identification, such as a password. These new layers of SCA authentication help verify user’s identities more confidently and reduces the risk of fraud for you and your customers.
How SCA can improve customer experience
Since SCA was implemented in 2021, merchants need to ensure that their transactions meet this requirement while still providing a frictionless checkout. When coupled with a comprehensive payment strategy, implementing SCA to meet PSD2 requirements can positively impact user experience.
Create an exemption strategy
SCA must be used for all remote electronic transactions unless an exemption applies. Exemptions include (but are not limited to), Transaction Risk Analysis (TRA), low-value payments (equal to/below €30 with further conditions applying), reoccurring transactions and transactions with trusted beneficiaries (white listing).
Utilize EMV 3D Secure 2.0 (EMV 3DS 2.0)
EMV 3DS 2.0 helps comply with SCA (and with other global regulations) by gathering up to 150 data points for each transaction. With EMV 3DS 2.0 you can minimize SCA friction and combat fraudulent transactions while safely increasing approval rates and reducing false declines.
Optimize your authentication strategy
As the industry evolves, so should your authentication strategy. Connect with our payment solution team to develop a more effective payment solution strategy for your business.
See the SCA authentication flows